Organizations retiring computers, servers, hard drives, and other storage devices must ensure sensitive information cannot be recovered or accessed by unauthorized parties. Simply deleting files or reformatting a device may not be enough to protect confidential data.
The NIST Special Publication 800-88 provides guidelines for media sanitization, helping organizations choose appropriate methods to remove data based on its sensitivity, the type of storage media, and how the device will be used or disposed of.
In this guide, we’ll explain what NIST 800-88 means, how it works, and why documented and compliant data destruction is important for organizations managing sensitive information.
What is NIST 800-88?
NIST 800-88, formally known as Guidelines for Media Sanitization, is a publication from the National Institute of Standards and Technology (NIST). It outlines three NIST 800-88 data destruction methods for making data stored on electronic media inaccessible to unauthorized users.
The guidelines cover a range of storage technologies, including hard disk drives (HDDs), solid-state drives (SSDs), USB drives, magnetic tapes, and mobile devices. They help organizations determine how to sanitize media before reusing, transferring, recycling, or permanently disposing of it.
NIST 800-88 is particularly relevant to federal agencies and defense contractors handling Controlled Unclassified Information (CUI). Other organizations, including healthcare providers, financial institutions, government agencies, and enterprises, also use its guidance to strengthen data security and support their compliance programs.
Learn more:
How to Build a Data Destruction Policy That Protects Your Organization
What are the three NIST 800-88 data destruction methods?
NIST 800-88 identifies three primary approaches to media sanitization: Clear, Purge, and Destroy. Each offers a different level of protection and supports different storage and disposition requirements. The appropriate NIST 800-88 data destruction method depends on the sensitivity of the information, the capabilities of the storage device, and whether the media needs to remain usable.
1. Clear
Clear uses logical techniques to remove data from user-addressable storage locations. Common approaches include data erasure, overwriting data or using supported device reset functions.
This method is designed to protect against basic, non-invasive data recovery attempts. The storage device generally remains functional and can be reused after the process is completed and verified.
When is Clear appropriate?
Clear may be suitable when devices are being redeployed within an organization or reused in an environment with compatible security requirements. It is generally intended for lower-sensitivity data when the selected method meets the organization’s sanitization requirements.
2. Purge
Purge uses more thorough logical or physical techniques to make data recovery infeasible, even when advanced laboratory methods are considered.
Depending on the device and its capabilities, Purge methods may include cryptographic erase or supported device-specific sanitization commands. Degaussing may also be applicable to certain magnetic media, but it is not suitable for flash-based SSDs.
Purge provides a stronger level of protection than Clear while potentially allowing the device to remain usable. The outcome depends on the media type and the method selected.
When is Purge appropriate?
Purge may be appropriate when devices will leave an organization’s control, be transferred to another party, or be prepared for remarketing while still retaining potential reuse value.
3. Destroy
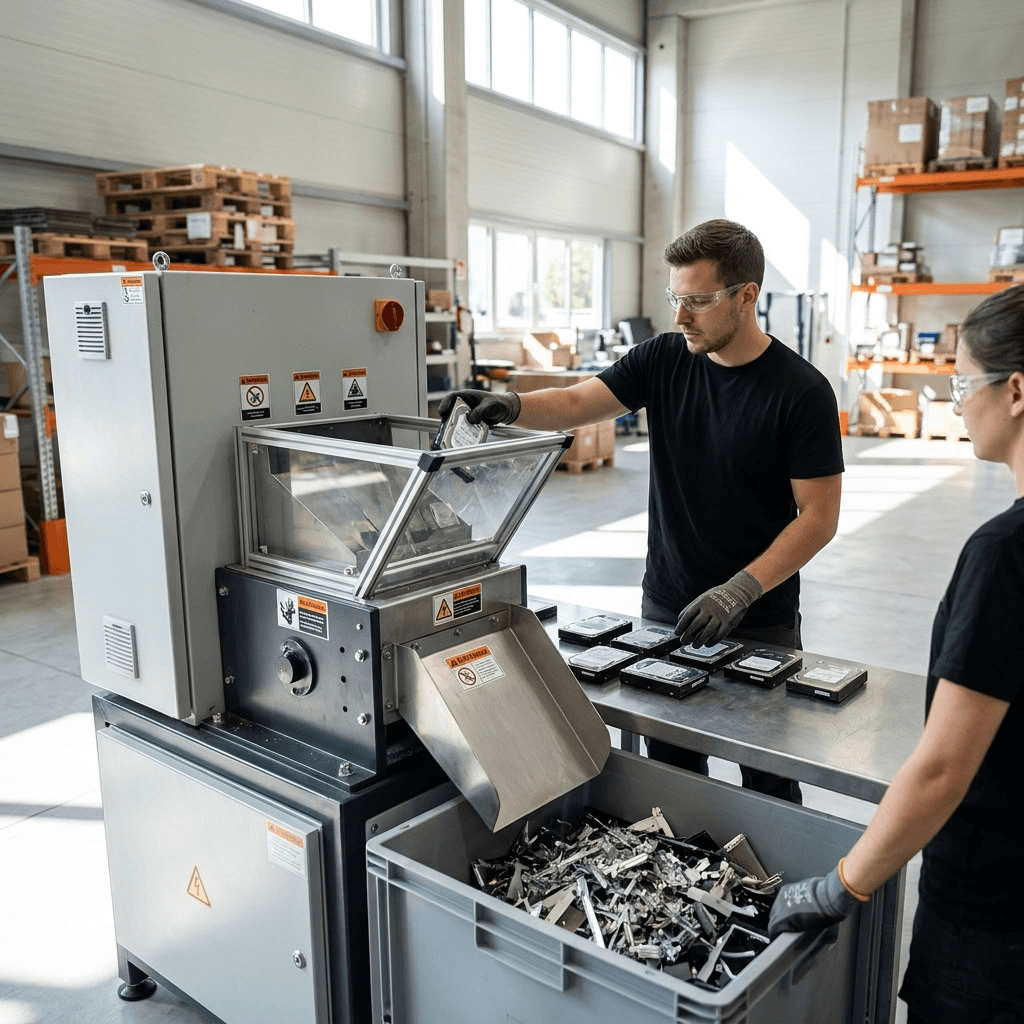
Destroy involves physically rendering storage media unusable so that the data cannot be recovered using the intended data destruction service.
Some physical destruction techniques can include hard drive shredding and pulverization. The appropriate NIST 800-88 data destruction method and asset size depend on the type of media and security requirements of the organization.
When is Destroy appropriate?
Destroy may be appropriate for damaged or end-of-life assets, devices that cannot be reliably sanitized through other methods, or information requiring physical destruction under an organization’s security procedures.
How do you choose the right NIST 800-88 data destruction method?
Choosing a NIST 800-88 media sanitization method requires more than deciding whether to wipe or shred a hard drive. Organizations should assess the information being protected, the capabilities of the media, and the device’s intended destination.
Consider these factors before selecting a method:
- Data sensitivity: Determine whether the media contains general business information, personal information, CUI, or other sensitive data.
- Storage technology: Confirm whether the device is an HDD, SSD, flash-based device, or another type of storage media.
- Future use: Decide whether the device will be reused internally, transferred to another organization, remarketed, recycled, or destroyed.
- Security requirements: Review applicable contracts, policies, and regulatory obligations to determine the required level of sanitization.
- Verification and documentation: Establish how the organization will confirm that sanitization was completed and retain evidence for future audits.
Learn more:
What’s the Difference Between Hard Drive Destruction, Hard Drive Erasure, and Data Deletion
Why is NIST 800-88 Compliance important?
Retiring IT hardware carries severe data exposure risks if assets aren’t properly sanitized. Following NIST 800-88 standards ensures your data is irreversibly destroyed using verified data destruction methods.
Throughout the process, your ITAD partner should have a strict chain of custody and secure ITAD client portal to track your assets from pickup to final disposition, delivering complete audit-ready accountability through detailed sanitization logs and Certificates of Destruction.
Learn more:
Importance of a Secure Chain of Custody Process for End-of-Life Data Destruction
What documentation should a NIST 800-88 data destruction process include?
Data destruction is not complete from an accountability perspective simply because a device has been wiped or physically destroyed. Organizations should also retain evidence of the work performed. Depending on the method and service, useful documentation may include:
Certificate of Destruction: Records identifying the processed media, its serial number, the sanitization method, and relevant processing details.
Sanitization verification reports: Documents confirming the outcome of Clear or Purge procedures and recording applicable verification results.
Chain of custody records: Documents tracking media from collection and transport through processing and final disposition, including relevant handoffs.
Asset inventory: A record of the devices collected and processed, helping reconcile equipment against internal asset lists.
Additional audit records: Where required, supporting records may include destruction logs, witness documentation, or video evidence.
The documentation should match the organization’s security requirements and provide a clear record of how the media was handled.
NIST 800-88 data destruction services from Keystone
By selecting an appropriate sanitization method, verifying the outcome, and maintaining supporting documentation, organizations can reduce the risks associated with residual data and strengthen their ITAD processes.
For organizations that need NIST 800-88-aligned data destruction, the appropriate process should be established according to the applicable requirements, available sanitization methods, and verification procedures. Ask Keystone about the specific methods, documentation, and service capabilities available for your project.
Learn more:
IT Asset Lifecycle Management Best Practices: A Complete Guide for Businesses and Organizations
Risks of Improper IT Asset Disposal: Why Secure Data Destruction Matters
3 Reasons Why Hard Drive Destruction is Beneficial to Your Business
Explore more:
Hard drive destruction
Data erasure
IT asset value recovery
E-waste recycling